Stop Writing Policy, Start Manufacturing Evidence: A 90-Day Room for UK Zero-Trust Assurance
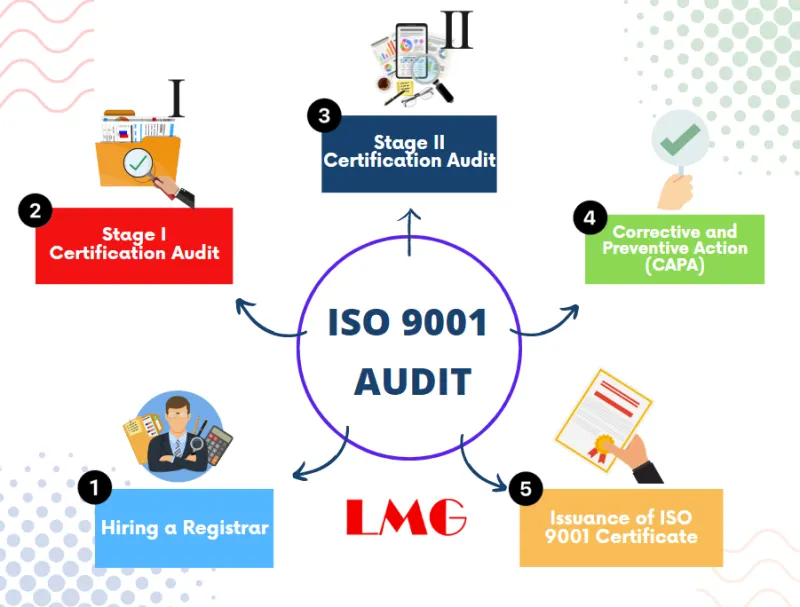
Photo: audit documents folders compliance review office desk professional, via lmgnewyork.com
Ask a UK technology leader to describe their zero-trust posture and you will usually get a confident paragraph. Ask them to prove three specific claims from that paragraph, with timestamps, and the conversation changes register. Somewhere between the architecture deck and the audit committee sits a gap that no amount of additional policy will close: the gap between what the organisation believes it does and what it can produce on request.
This is an argument for building less documentation and manufacturing more evidence.
The uncomfortable economics of assurance
Most organisations have policy in abundance. What they lack is a defensible trail linking intent to operation. When an insurer asks how device compliance is enforced, when a customer's security team issues a due diligence questionnaire, when a regulator under operational resilience or data protection expectations requests an account of controls, the response is typically assembled under pressure from ticket exports, screenshots pasted into a document, and a supplier email from eighteen months ago. That response is expensive, inconsistent and — crucially — unrepeatable.
An evidence room inverts the effort. Instead of assembling proof after the question arrives, you agree in advance what good looks like, automate its capture, and review it on a rhythm. Ninety days is enough to build a first version, provided the scope is ruthless.
Rule one: one room, not five
Most large UK organisations already hold the artefacts required. They are distributed across an ITSM platform, an identity team's dashboard, a vulnerability scanner, a procurement shared drive and a risk register that only the risk function can open. The first task is not collection but consolidation: a single controlled location, with a fixed structure, an index, and access rights that satisfy both the security team and a visiting auditor.
Structure the room against four domains that map to how zero-trust is actually assessed — identity, device, network, supplier — and add a fifth index for the controls framework the organisation has chosen to be judged against, whether that is ISO/IEC 27001:2022, the NCSC Cyber Assessment Framework, Cyber Essentials Plus or a sector scheme such as the NHS Data Security and Protection Toolkit.
Days 1–30: identity and access
The first month produces the smallest number of artefacts with the highest assurance value. In practice: an export of conditional access or equivalent policy definitions, with version history; a coverage report showing the proportion of the workforce and of privileged accounts using phishing-resistant authentication; a joiner-mover-leaver reconciliation sample with the ticket references; and a list of non-human identities — service accounts, API clients, workload credentials — with owners and review dates.
Two disciplines matter here. Every artefact must carry a generation timestamp and a named owner. And samples must be chosen by a rule, not by convenience: an auditor will ask how the sample was drawn, and 'the ones that looked fine' is not an answer.
Days 31–60: devices and network
Month two shifts to the estate. The minimum set is a device compliance attestation showing posture checks and enforcement action taken, a patch and vulnerability summary with remediation timelines against your own stated standard, and a current network segmentation diagram that reflects deployed policy rather than design intent. Add the rule sets behind the segmentation — firewall policies, microsegmentation definitions, access control lists — and a recent test showing that a denied path is genuinely denied.
This last item is where most rooms are thin. Diagrams describe intent; a test record describes behaviour. One reviewed negative test per quarter is worth more than a hundred pages of architecture.
Days 61–90: suppliers, incidents and the first review
The final month addresses the dependencies the organisation does not control. Collate supplier assurance questionnaires with dates and any exceptions accepted, tier suppliers by the data and access they hold, and record the contractual hooks that allow you to demand updated evidence. Alongside this, gather incident response rehearsal reports, tabletop outputs and the corrective actions arising — again with owners and closure evidence.
Then hold the first review. Not a walkthrough of the folder, but a challenge session: which artefacts are missing, which are stale, which claims cannot be supported. Expect the first pass to be uncomfortable. That discomfort is the product.
| Artefact group | Owner | Refresh cadence |
|---|---|---|
| Identity policy definitions and MFA coverage | Head of IAM | Monthly |
| Non-human identity register | Platform engineering lead | Quarterly |
| Device compliance and patch posture | Endpoint engineering lead | Monthly |
| Segmentation rule sets and negative tests | Network security lead | Quarterly |
| Supplier assurance and exceptions | Procurement risk lead | Annual, with quarterly exceptions review |
| Incident rehearsal outputs | Head of resilience | After each exercise |
| Framework mapping index | Risk and compliance lead | Twice yearly |
Make the evidence survive contact
Three properties determine whether a room withstands scrutiny. Integrity: artefacts should be stored immutably or with hash verification, so that a document produced in November cannot be quietly amended in March. Provenance: each item should record where it came from and by what method it was generated. Retention: align the retention period with the longest applicable obligation — sector rules, contractual terms, insurer requirements — and say so explicitly in the index.
Equally important is what to leave out. Do not stuff the room with raw telemetry dumps, unredacted personal data or marketing-grade architecture diagrams. A room that takes four hours to navigate will not be used, and one that holds unnecessary personal data creates a liability under UK GDPR while attempting to demonstrate good practice.
The cultural point
An evidence room is not a compliance artefact; it is a management instrument. Once a control has a named owner, a refresh cadence and a visible gap list, conversations about zero-trust maturity stop being rhetorical. Arguments about budget become arguments about specific missing proofs. Board reporting gets shorter and sharper.
The instinct in most organisations is to answer a request for proof by writing another policy. Resist it. Policy states what should happen. Evidence shows what did. Only one of those survives an audit, an insurance renewal or a customer's due diligence team — and it is the one worth building in the next ninety days.